• Home
  • Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) | Refresh
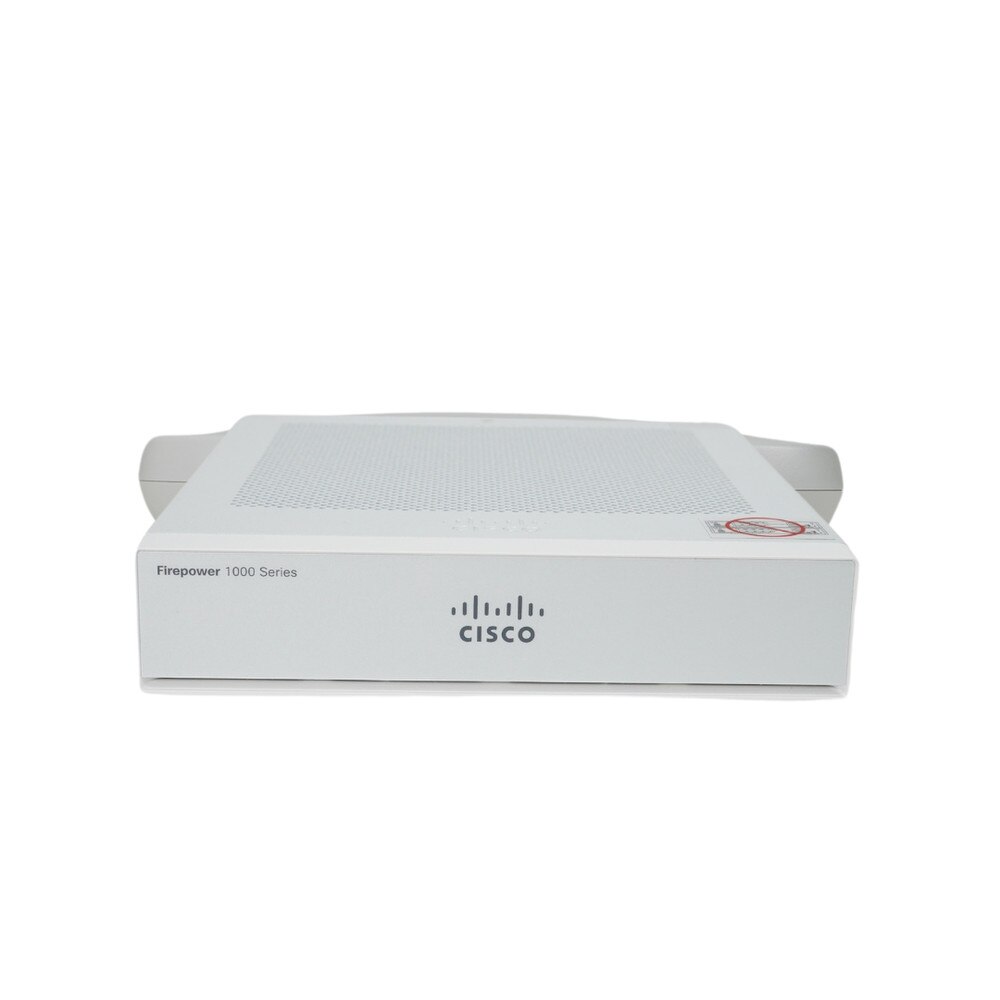
Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) | Refresh

Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) | Refresh

SKU: FPR1010-NGFW-K9-RF
(0)No Reviews yet

📦 What's in the Box?
  • ✅Cisco Firepower 1010 Chassis
  • ✅External Power Supply
  • ✅Power Cord
  • ✅USB Console Cable
  • ✅Product Documentation
Same Day Shipping - Arrives in 3-5 Business Days
30-day Returns

Call for Availability

For immediate assistance call our support team at 973-808-4588. For additional information, send an email to website@telquestintl.com.

Overview

Overview of Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) | Refresh

The Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) is a compact desktop security device designed to safeguard retail establishments, branch offices, small offices and dispersed business networks. Application visibility and control, intrusion prevention, URL filtering, malware defense choices, VPN connectivity and centralized policy management via Cisco Firepower Threat Defense are all combined with stateful firewalling. The Cisco Firepower 1010 enables businesses secure wired and connected edge devices without the need for a sizable rack-mounted security platform due to its eight Gigabit Ethernet RJ45 interfaces, fanless desktop compact size and integrated PoE functionality on specific ports. IT organizations can enforce uniform network security rules in branch and small-office settings with the aid of Firepower Threat Defense, which offers unified visibility into apps, users, threats and online activities.


Key Features of Cisco Firepower 1010 Next-Generation Firewall


• Cisco Firepower 1010 next-generation firewall appliance with Cisco Firepower Threat Defense software image.

• Eight 1GbE RJ45 Ethernet interfaces provide flexible LAN, WAN, DMZ and segmented network connectivity.

• Desktop, fanless appliance design supports quiet deployment in branch offices, retail sites and small business environments.

• Up to 890 Mbps firewall plus application visibility and control throughput, with approximately 880 Mbps when intrusion prevention is enabled under Cisco’s specified performance testing.

• Up to 100,000 concurrent sessions and up to 6,000 new connections per second with application visibility and control enabled.

• Application Visibility and Control identifies and manages thousands of applications, users, websites and geolocations for more granular security policies.

• Next-Generation Intrusion Prevention System detects and blocks known exploits, malicious traffic and intrusion attempts.

• URL filtering supports web-use policies using more than 80 URL categories and a database covering hundreds of millions of categorized URLs.

• Malware Defense for Networks and malware sandboxing options extend protection against file-based and advanced threats.

• TLS decryption capability supports deeper inspection of encrypted traffic, with up to 195 Mbps TLS throughput.

• IPsec VPN performance supports secure site-to-site or remote-access connectivity, with up to 75 VPN peers.

• Active/standby high availability supports resilient firewall deployment.

• Local management through Cisco Firepower Device Manager and centralized configuration, monitoring, logging and reporting through Cisco Firewall Management Center.

• Cisco Defense Orchestrator can support cloud-based policy and device management workflows.

• External 60W AC power adapter and low system power draw support efficient branch security deployment.


Benefits of Cisco Firepower 1010 Next-Generation Firewall


🗹 Protects branch, small-office, and retail networks with a unified next-generation firewall platform rather than separate firewall, IPS, web-filtering and application-control tools.

🗹 Gives administrators meaningful visibility into the applications and users consuming network resources, allowing more precise policies than port- and protocol-only firewall rules.

🗹 Helps block exploits, suspicious traffic, malware delivery attempts and unsafe web destinations before threats move deeper into the organization.

🗹 Supports encrypted-traffic inspection, helping security teams apply policy controls to a significant portion of modern HTTPS-based business and web traffic.

🗹 Connects remote offices securely using IPsec VPN tunnels, making it easier to extend corporate security policies across distributed sites.

🗹 Fits quietly on a desk, shelf, or small network cabinet because of its compact, fanless design.

🗹 Supports centralized management and reporting through Cisco Firewall Management Center, reducing the administrative burden of maintaining multiple distributed security appliances.

🗹 Provides a scalable entry point into Cisco Secure Firewall and Firepower Threat Defense environments for organizations standardizing security policy across locations.

Specifications

Specifications for Cisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image (FPR1010-NGFW-K9) | Refresh

ManufacturerCisco
Manufacturer Part NumberFPR1010-NGFW-K9-RF
Product NameCisco Firepower 1010 Next-Generation Firewall with Firepower Threat Defense Software Image
Product TypeFirewall
Software imageCisco Firepower Threat Defense (FTD)
Primary deploymentSmall office, branch office, retail, and distributed enterprise edge
Form factorCompact desktop appliance; optional rack-mount shelf supports 2RU installation
Firewall deployment modeRouted and transparent firewall modes
High availabilityActive/standby
ClusteringNot supported
Integrated network data ports8 × 10/100/1000BASE-T Gigabit Ethernet RJ45 ports
Integrated switchMarvell SOHO 88E6390 Layer 2 switch
Data-port identificationGigabitEthernet 1/1 through GigabitEthernet 1/8
Data-port featuresAuto-negotiation, auto-MDI/MDIX, and MDI/X compliance
Dedicated management port1 × 10/100/1000BASE-T Gigabit Ethernet RJ45; restricted to network-management access
Console interface1 × RJ45 console port
USB management interface1 × USB Mini-B port for management access from an external system
USB host port1 × USB 3.0 Type-A port for external storage or other supported external devices
PoE capabilityIntegrated PoE+ support; up to 60W available for connected powered devices, subject to power budget
Threat Defense / NGFW throughput890 Mbps
IPS throughput900 Mbps
Firewall plus AVC throughput, 1024-byte packets650 Mbps
Firewall plus AVC plus IPS throughput, 1024-byte packets650 Mbps
NGIPS throughput, 1024-byte packets650 Mbps
Stateful firewall throughput2 Gbps
Stateful multiprotocol firewall throughput1.4 Gbps
TLS decryption throughput195 Mbps
IPsec VPN throughput400 Mbps
Maximum concurrent sessions with AVC100,000
Maximum new connections per second with AVC6,000
Maximum firewall new connections per second25,000
Maximum VPN peers75
Application visibility and controlIncluded with FTD capabilities
Intrusion preventionCisco Next-Generation IPS available with appropriate licensing
URL filteringAvailable; more than 80 URL categories and more than 280 million categorized URLs
Malware protectionCisco Malware Defense for Networks available with appropriate licensing
Malware sandboxingCisco Malware Analytics sandboxing available with appropriate licensing
Security intelligenceCisco Security Intelligence for IP, URL, and DNS threat intelligence
Local managementCisco Firepower Device Manager
Centralized managementCisco Firewall Management Center
Cloud managementCisco Defense Orchestrator support
Management protocolsHTTPS, SSH, SNMP, Syslog, and REST API support, subject to deployed software and configuration
Routing supportIPv4 and IPv6 routing; static and dynamic routing features available in FTD
VPN servicesIPsec site-to-site VPN and supported remote-access VPN services
Network segmentationVLAN interfaces, subinterfaces, zones, access-control policy, NAT, and routing policies
CPU1 × 4-core Intel processor
System memory8 GB DDR4 DRAM
Internal boot storage8 GB internal boot partition
CoolingPassive, fanless; side-to-side airflow
System power consumption30W, excluding connected PoE devices
Maximum power-supply capacity55W maximum from the appliance power supply
PoE power capacityUp to 60W PoE+ for connected devices
Power supplyExternal AC power adapter
AC input voltage100–240 VAC
AC input frequency50–60 Hz
DC input12 VDC
Dimensions, H × W × D46.2 × 199.4 × 205 mm (1.82 × 7.85 × 8.07 in.)
Chassis weight1.36 kg (3 lb.)
Operating temperature0°C to 40°C (32°F to 104°F)
Non-operating / storage temperature-40°C to 70°C (-40°F to 158°F)
Operating humidity10% to 90%, noncondensing
Operating altitude0 to 10,000 ft (0 to 3,000 m)
Non-operating altitude0 to 15,000 ft (0 to 4,570 m)
Regulatory complianceDesigned to meet applicable Cisco safety, EMC, and environmental standards for the Firepower 1000 Series
Included hardwareFirepower 1010 appliance and external power adapter

User Guides

Frequently Asked Questions

Cisco Firepower 1010 Next-Generation Firewall
Frequently Asked Questions (FAQ's)


How many Ethernet interfaces does the Cisco Firepower 1010 provide?

The Firepower 1010 provides eight Gigabit Ethernet RJ-45 data interfaces, giving administrators flexibility to configure WAN, LAN, DMZ, guest and other network zones.

What firewall throughput does the Firepower 1010 support?

Cisco specifies up to 890 Mbps firewall plus Application Visibility and Control throughput using 1024-byte packets when running Threat Defense software.

What throughput is available when IPS is enabled?

With firewall, AVC and intrusion prevention enabled, Cisco lists up to 880 Mbps throughput for the Firepower 1010.

What is the NGIPS throughput of the Firepower 1010?

Cisco specifies up to 900 Mbps NGIPS throughput for the platform.

How much IPsec VPN throughput does the Firepower 1010 provide?

Cisco lists approximately 400 Mbps IPsec VPN throughput using 1024-byte TCP traffic with Fastpath.

How many VPN peers can the Firepower 1010 support?

The platform supports up to 75 VPN peers, making it suitable for small-business, branch and distributed connectivity requirements.

How many concurrent sessions can the firewall handle?

Cisco specifies up to 100,000 concurrent sessions with AVC enabled on the Firepower 1010.

How many new connections per second does it support?

The appliance supports approximately 6,000 new connections per second with AVC enabled.

Does the Firepower 1010 support Power over Ethernet?

Yes. The Firepower 1010 platform includes two PoE+ capable Gigabit Ethernet ports, allowing compatible devices to receive data and power through Ethernet.

Is the Firepower 1010 fanless?

Yes. The Firepower 1010 uses a fanless design, helping keep operation quiet in offices, branch locations, retail environments and other occupied spaces.

Can the Firepower 1010 be managed locally?

Yes. Administrators can use Firewall Device Manager to configure and manage Threat Defense directly on the appliance through a browser-based interface.

Can the Firepower 1010 be centrally managed?

Yes. Cisco supports centralized management through Firewall Management Center and current documentation also describes cloud-delivered management options.

Does the Firepower 1010 support application visibility and control?

Yes. Cisco AVC functionality can identify and control thousands of applications while also incorporating information about users, geolocations and websites into security policy decisions.

Does it provide intrusion-prevention functionality?

Yes. Cisco IPS functionality is available with Threat Defense and can help identify malicious activity, detect endpoints and infrastructure and correlate security events.

Does the Firepower 1010 support threat intelligence?

Yes. Cisco Security Intelligence provides threat-awareness capabilities using IP, URL and DNS intelligence to help identify and control connections involving known or suspected malicious destinations.

Can the Ethernet ports be used as switch ports?

Yes. Firepower 1010 interfaces can be configured for supported switch-port and VLAN scenarios under Threat Defense. Cisco documentation notes that switch ports on the same VLAN can communicate using hardware switching.

Can the Firepower 1010 separate different network zones?

Yes. Its multiple interfaces and VLAN capabilities allow administrators to design separate security zones for internal users, servers, guest networks, DMZ resources and other network segments.

Does FPR1010-NGFW-K9 ship with the Threat Defense software image?

Yes. The FPR1010-NGFW-K9 SKU is identified by Cisco as the Firepower 1010 hardware configuration with the FTD/Threat Defense software image.

Is additional licensing required for every advanced security feature?

Some capabilities are included with the platform, while other advanced services and threat-protection functions can depend on the licensing or subscription configuration purchased. Cisco's current deployment documentation specifically instructs administrators to obtain the appropriate licenses before completing setup.

What types of deployments are best suited for the Firepower 1010?

Cisco positions the Firepower 1000 Series for small offices and remote branches. The Firepower 1010 is particularly appropriate where organizations need compact next-generation firewall protection, VPN connectivity, multiple Gigabit interfaces and flexible local or centralized management.

Ratings & Reviews

No reviews available

Be the first to Write a Review